AI for Enterprise Security
Cloud Misconfigurations Found. Investigated. Prioritized.
Crogl delivers AI cloud security posture management: continuously monitoring your cloud environments, investigating every misconfiguration with full context, and delivering prioritized remediation recommendations. Your cloud posture never drifts without your team knowing.
Crogl handles the investigation. The analyst makes the call.
The Cloud Security Gap
Your cloud changes faster than your team can review it.
Cloud environments change thousands of times per day, with new resources provisioned, configurations modified, and permissions adjusted. Each change is a potential security event. Most go unreviewed until the next scan cycle, or until something breaks.
The most common cloud breaches don't involve sophisticated attacks. They exploit simple misconfigurations that sat undetected for days, weeks, or months.
80%
Of cloud breaches involve misconfiguration, not sophisticated exploitation
Thousands
Of cloud configuration changes daily that security teams cannot manually review
Minutes
Between a misconfiguration and exploitation in automated attack campaigns
The Crogl Approach
Continuous monitoring. Automatic investigation. Prioritized remediation.
Continuous Cloud Configuration Monitoring
Crogl monitors AWS, Azure, and GCP continuously. Misconfigurations, policy violations, and drift from your security baselines are detected as they happen. Not during scheduled scans. In real time.
Context-Rich Investigation of Every Finding
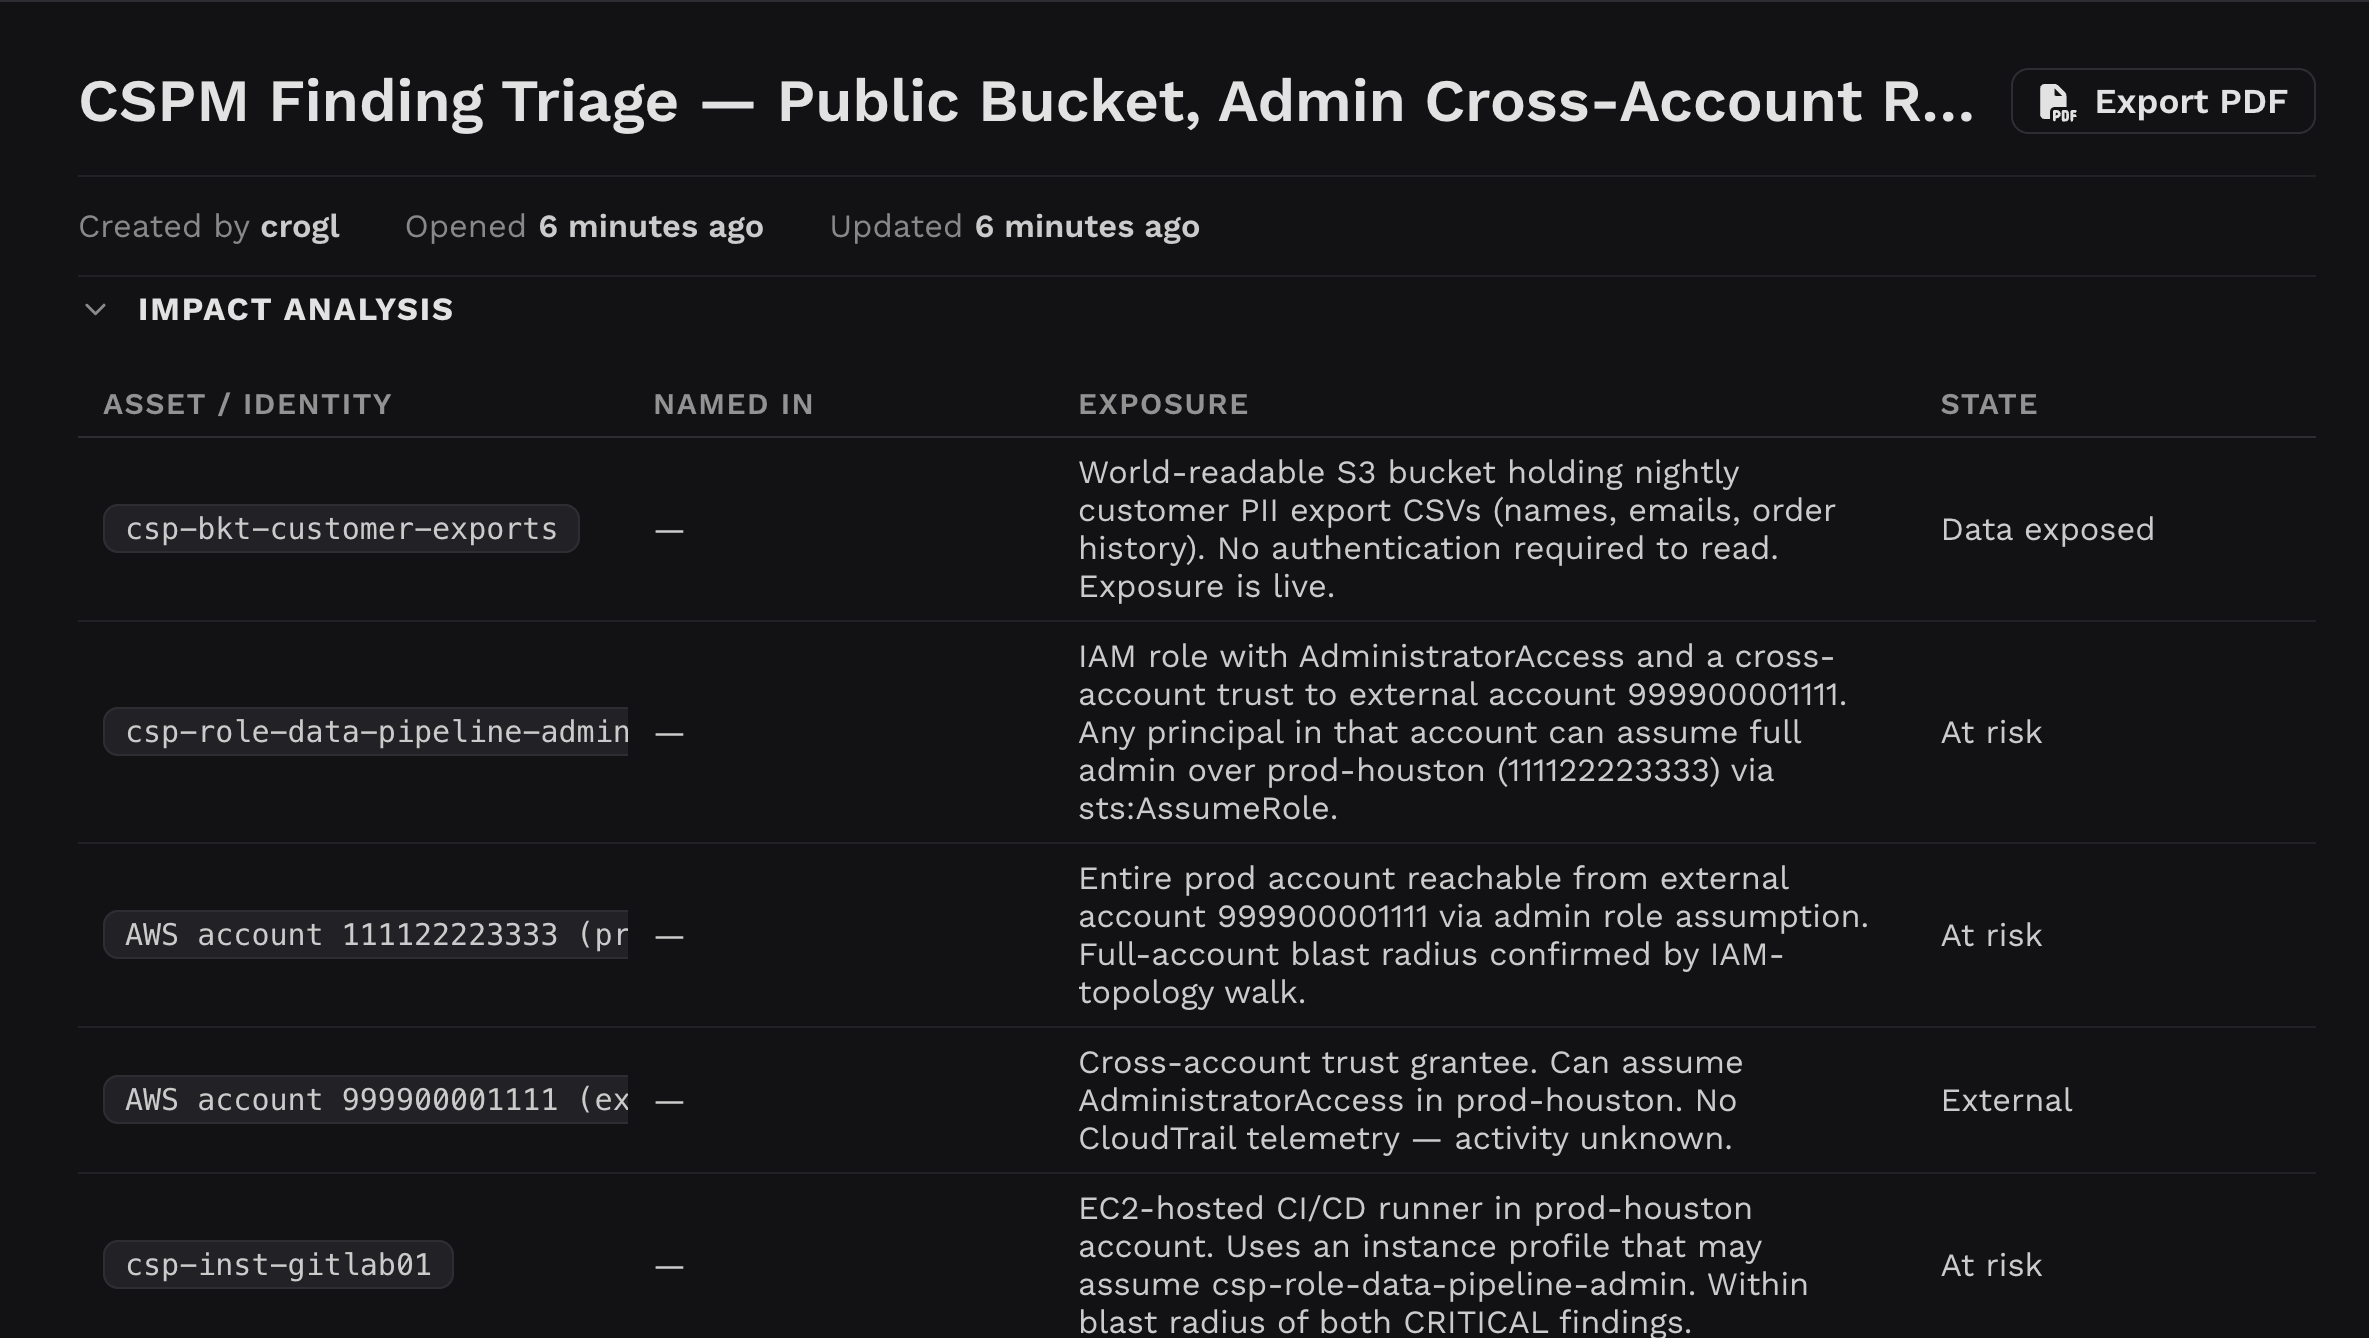
When Crogl detects a misconfiguration or policy violation, it doesn't just flag it. It investigates: who made the change, what it affects, whether it's been exploited, and what the blast radius would be. Your team gets a finding, not an alert.
Prioritized Remediation With Full Evidence
Each finding includes a prioritized remediation recommendation with full evidence: what to fix, why it matters, and what the risk is if it's not addressed. Your cloud team acts on findings, not on a spreadsheet of flagged configurations.
What Crogl Delivers
Real-Time Misconfiguration Detection
Detect cloud misconfigurations as they happen, not during the next scan cycle. Public S3 buckets, overly permissive IAM roles, exposed endpoints, and security group violations caught in real time.
Cross-Cloud Visibility
Unified posture monitoring across AWS, Azure, and GCP. One investigation platform for your entire cloud footprint, no switching between cloud-native tools or losing context at the boundary.
Compliance Mapping
Cloud posture findings mapped directly to CIS benchmarks, SOC 2, ISO 27001, and your organization's specific security policies. Compliance status is always current, not reconstructed for audits.
Drift Detection and Remediation Tracking
Track configuration drift from your approved baselines and monitor remediation progress. Know exactly which findings are open, which are in progress, and which have been verified as resolved.
Monitors Your Cloud Environments
“Every cloud. Every configuration. Continuously monitored.”
Frequently asked questions
Which clouds does Crogl monitor?
Crogl monitors AWS, Microsoft Azure, and Google Cloud continuously, in one investigation workflow instead of separate cloud-native consoles. It detects misconfigurations, policy violations, and drift from your security baselines as they happen, including public S3 buckets, overly permissive IAM roles, exposed endpoints, and security group violations, then investigates each finding with full context.
Who makes the cloud configuration change?
Your cloud team. Each Crogl finding comes with a prioritized remediation recommendation and full evidence: what to fix, why it matters, and the risk if it isn't addressed. Crogl investigates who made the change and what it affects, then tracks remediation from open to in progress to verified as resolved.
Which frameworks are cloud findings mapped to?
Crogl maps cloud posture findings to CIS benchmarks, SOC 2, ISO 27001, and your organization's own security policies. Because findings are mapped as they're detected, the mapping stays current instead of being reconstructed before each audit. Crogl documents the evidence, and your auditors make the determination.
See Your Cloud Posture Clearly
What misconfigurations are sitting in your cloud right now?
We'll show you how Crogl monitors your cloud environments continuously, and investigates every finding with full context.
Deployed across AWS, Azure, and GCP environments at enterprise scale.